Check out the latest research from IONIX: NEW! State of the WAF Report

New CVE Detected

CVE-2026-123710 – Unauthenticated Signing Key Takeover / Authentication Bypass – Red Hat Quay 3 and

Be the first to know when new zero-days emerge:

Summary

CVE-2026-123710 is a critical improper input validation flaw (CWE-1287) in Red Hat Quay that lets an unauthenticated remote attacker take over the registry’s token signing by installing their own service signing key. It affects Red Hat Quay 3 and Red Hat Quay 5 container images and has a CVSS v3.1 score of 9.8 (Critical).

Technical details

  • Root cause: Improper validation of specified type of input (CWE-1287) in the Quay service key rotation endpoint, which accepts an anonymous registry token whose audience the client controls.
  • Trigger conditions: No authentication or user interaction is required. The client obtains an anonymous registry token with an audience it controls and presents it to the service key rotation endpoint.
  • Attack vector: Network, low complexity.
  • Impact: The attacker installs its own approved signing key with no expiry. Per the CVE record, this enables access to private images and modification of repository tags, with high impact on confidentiality, integrity and availability.
  • No public exploit code or known exploitation was confirmed at the time of writing.

Affected software

  • Red Hat Quay 3 (quay/quay-rhel8, quay/quay-rhel9)
  • Red Hat Quay 5 (quay/quay-rhel9)

Severity

  • CVSS v3.1 base score: 9.8 (Critical)
  • Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H

Mitigation and recommended actions

  • Immediate: No fixed version was listed in the CVE record at the time of writing. Monitor the Red Hat advisory for CVE-2026-123710 and apply patches as soon as they are released.
  • Until a patch is available: restrict network access to the service key rotation endpoint to trusted internal or administrative networks, and review the registry’s service keys for unexpected or non-expiring entries.

References

Are you exposed?

Get a free report of your organization’s exposure to this CVE and threat

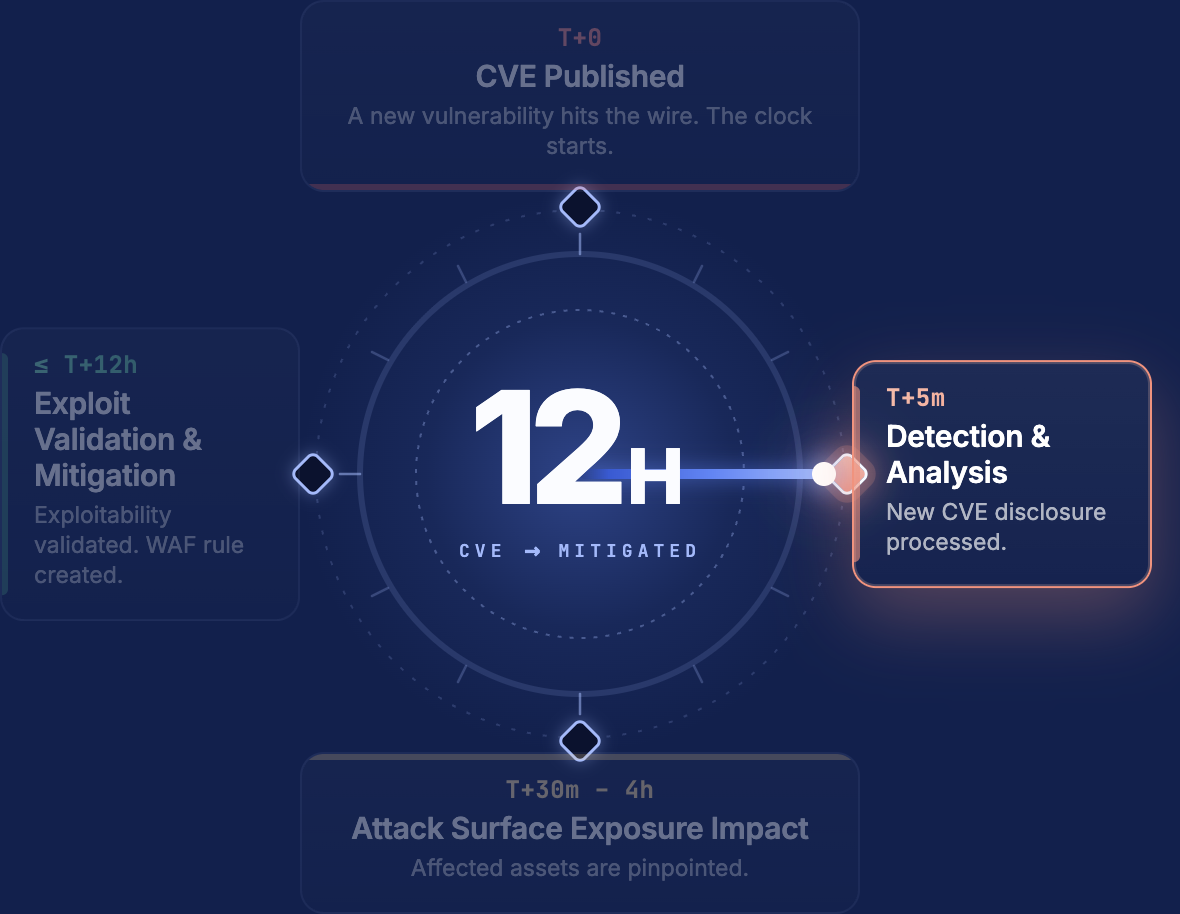
How IONIX’s External Exposure Management Platform Detects and Validates
Zero-Days to Shrink MTTR

1

Map your entire attack surface (continously)

IONIX uses multi-factor discovery methods, including DNS analysis, certificate mapping, metadata inspection, and more, to automatically map every internet-facing asset across your environment. This includes cloud instances, third-party platforms, shadow IT, and even forgotten infrastructure that traditional tools miss.

2

Monitor for new CVEs

Dozens of threat intel feeds using agentic technology are continuously analyzed to detect the appearance of proof-of-concept code, exploit kits, and indicators of active targeting. IONIX goes further by applying AI to proactively evaluate whether emerging vulnerabilities are likely to be exploited, even before PoCs go public.

3

Identify Potential External Exposures

Not all CVEs matter. IONIX filters vulnerabilities by asking attacker-centric questions: Can it be reached from the internet? Does it require authentication? Is it being exploited in the wild? This dramatically reduces noise and focuses teams on threats that can actually be weaponized.

4

Create Safe, Scalable Exploit Validations

IONIX transforms real-world PoCs into safe, non-intrusive test payloads that can be run in production environments without disruption. These simulations are precisely targeted to the systems that are vulnerable, ensuring rapid validation without unnecessary load.

5

Execute Exploit Validations

By combining context about software stack, versioning, exposure status, and reachability, IONIX ensures that only the right payloads are executed against the right assets, maximizing efficiency and minimizing risk.

6

Drive Fast and Actionable Remediation

Results are routed through integrations with ticketing, SOAR, and SIEM tools. Issues are written in plain language, bundled into remediation clusters, and prioritized based on asset criticality, exploitability, and blast radius. This shortens mean time to remediation (MTTR) and empowers teams to act with confidence.

Are you exposed?

Get a free report of your organization’s exposure to this CVE and threat

Subscribe to Threat Center RSS

Copy/paste the link below into your preferred RSS reader or follow these instructions to subscribe to Slack alerts.

Get Real-Time CVE Alerts to Your Email

Be the first to know when new zero-days emerge