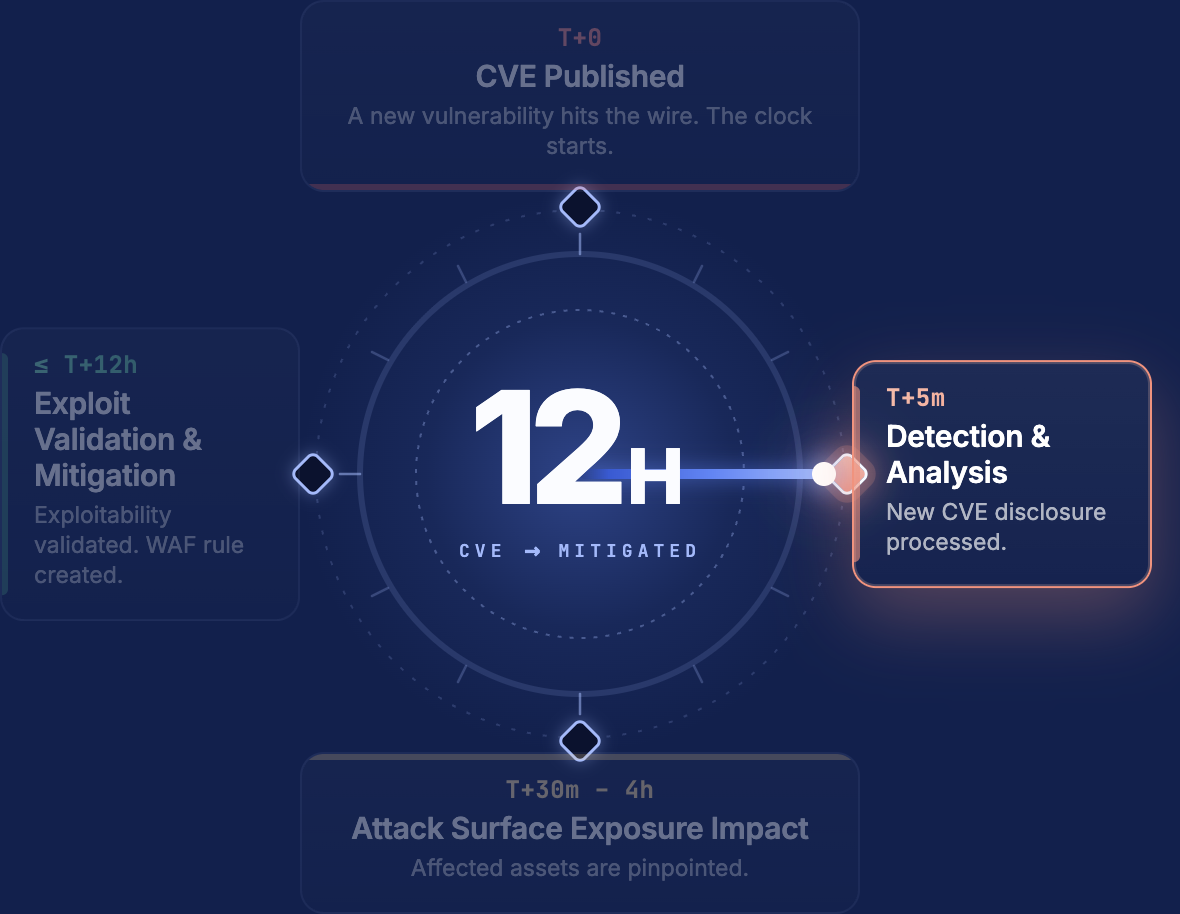
Live Exposure Defense: From CVE to Confirmed Exposure in 12 Hours – See more

New CVE Detected

CVE-2026-13249 – Unauthenticated RCE via Arbitrary File Upload – Honeywell PD45 Industrial Printer (

Be the first to know when new zero-days emerge:

Summary

CVE-2026-13249 is a critical unauthenticated Remote Code Execution vulnerability in the web management interface of the Honeywell PD45 Industrial Printer. The flaw allows an attacker to upload attacker-controlled files without any authentication, leading to execution of malicious files and commands on the device. The issue carries a CVSS v3.1 base score of 9.8 (Critical), reflecting network-exploitability with no authentication or user interaction required.

Technical details

  • Root cause: The web management interface fails to enforce authentication on a file upload function (CWE-306: Missing Authentication for Critical Function), and does not restrict the type of files that can be uploaded (CWE-434: Unrestricted Upload of File with Dangerous Type).
  • Trigger conditions: An attacker sends a file upload request to the printer’s web management interface without providing any credentials.
  • Attack vector: Network — the vulnerable interface is reachable over the network with no privileges or user interaction required (AV:N/AC:L/PR:N/UI:N).
  • Impact: Once uploaded, the malicious file can be leveraged to execute arbitrary OS commands (CWE-78: OS Command Injection), resulting in full compromise of confidentiality, integrity, and availability of the affected device.

Affected software

  • Honeywell PD45 Industrial Printer, firmware version F10.19.010040 and later versions prior to F10.22.030745.

Severity

  • CVSS v3.1 Base Score: 9.8 (Critical)
  • Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H

Mitigation and recommended actions

  • Immediate: Upgrade the Honeywell PD45 Industrial Printer firmware to version F10.22.030745 or later, which contains the fix for this vulnerability.
  • If immediate patching is not possible:
    • Restrict network access to the printer’s web management interface to trusted, segmented management networks only.
    • Do not expose the printer’s management interface directly to the internet.
    • Monitor for unexpected file upload activity or unusual outbound connections from affected devices.
    • Apply firewall rules or access control lists to limit inbound connections to the management interface to authorized administrative hosts.

References

Are you exposed?

Get a free report of your organization’s exposure to this CVE and threat

How IONIX’s External Exposure Management Platform Detects and Validates
Zero-Days to Shrink MTTR

1

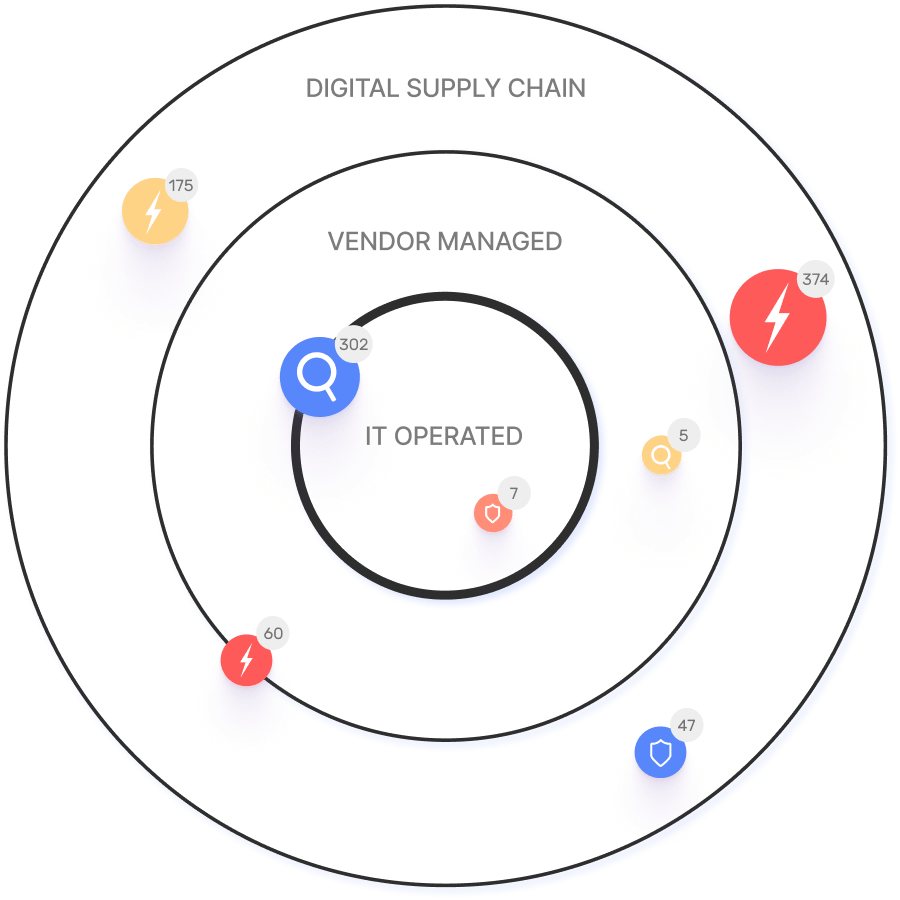
Map your entire attack surface (continously)

IONIX uses multi-factor discovery methods, including DNS analysis, certificate mapping, metadata inspection, and more, to automatically map every internet-facing asset across your environment. This includes cloud instances, third-party platforms, shadow IT, and even forgotten infrastructure that traditional tools miss.

2

Monitor for new CVEs

Dozens of threat intel feeds using agentic technology are continuously analyzed to detect the appearance of proof-of-concept code, exploit kits, and indicators of active targeting. IONIX goes further by applying AI to proactively evaluate whether emerging vulnerabilities are likely to be exploited, even before PoCs go public.

3

Identify Potential External Exposures

Not all CVEs matter. IONIX filters vulnerabilities by asking attacker-centric questions: Can it be reached from the internet? Does it require authentication? Is it being exploited in the wild? This dramatically reduces noise and focuses teams on threats that can actually be weaponized.

4

Create Safe, Scalable Exploit Validations

IONIX transforms real-world PoCs into safe, non-intrusive test payloads that can be run in production environments without disruption. These simulations are precisely targeted to the systems that are vulnerable, ensuring rapid validation without unnecessary load.

5

Execute Exploit Validations

By combining context about software stack, versioning, exposure status, and reachability, IONIX ensures that only the right payloads are executed against the right assets, maximizing efficiency and minimizing risk.

6

Drive Fast and Actionable Remediation

Results are routed through integrations with ticketing, SOAR, and SIEM tools. Issues are written in plain language, bundled into remediation clusters, and prioritized based on asset criticality, exploitability, and blast radius. This shortens mean time to remediation (MTTR) and empowers teams to act with confidence.

Are you exposed?

Get a free report of your organization’s exposure to this CVE and threat

Subscribe to Threat Center RSS

Copy/paste the link below into your preferred RSS reader or follow these instructions to subscribe to Slack alerts.

Get Real-Time CVE Alerts to Your Email

Be the first to know when new zero-days emerge