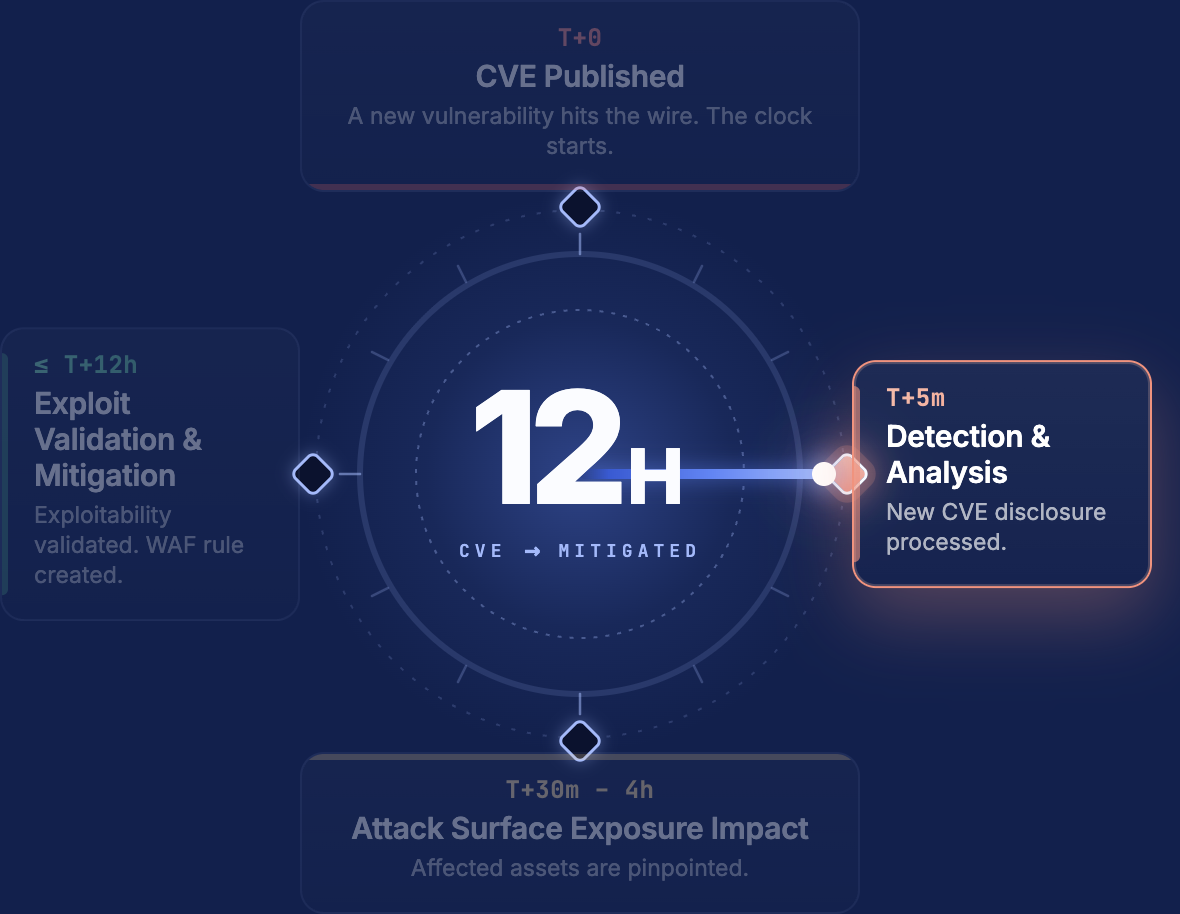
Live Exposure Defense: From CVE to Confirmed Exposure in 12 Hours – See more

New CVE Detected

CVE-2026-97360 – Unauthenticated Arbitrary File Read/Write/Delete (RCE potential) – Rejetto HFS2 2.0

Be the first to know when new zero-days emerge:

Summary

CVE-2026-97360 is a critical missing-authorization vulnerability (CWE-862) in Rejetto HFS2 (HTTP File Server, the legacy pre-Node.js codebase), affecting versions 2.0.0 through 2.4.0. The flaw allows a completely unauthenticated, remote attacker to read, write, append to, and delete arbitrary files anywhere the HFS process account can access on the underlying filesystem — not just inside the configured shared folder. The vulnerability carries a maximum CVSS v3.1 base score of 10.0.

Technical details

  • Root cause: HFS2’s macro/template dispatcher, which processes file-operation directives such as {.load.}, {.save.}, {.append.}, and {.delete.}, performs no authorization checks before executing the requested operation.
  • Contributing flaw: The internal path resolution function returns the supplied path unmodified whenever it contains no forward slash, allowing absolute filesystem paths (e.g., C:Windowswin.ini) to bypass the intended confinement to the shared directory.
  • Trigger conditions: An attacker submits a request that reaches HFS2’s template evaluation engine (for example via upload filename handling) and injects a file-operation macro referencing an absolute path.
  • Attack vector: Network, no authentication or user interaction required.
  • Impact: Full compromise of confidentiality, integrity, and availability of the host — arbitrary file read (information disclosure), arbitrary file write/append (which can be leveraged toward remote code execution), and arbitrary file deletion outside the shared directory.

Affected software

  • Rejetto HFS2 (HTTP File Server, legacy Delphi/Pascal-based branch) versions 2.0.0 through 2.4.0, inclusive
  • The newer Node.js-based HFS 3.x rewrite is a separate, actively maintained codebase and is not affected by this issue

Severity

  • CVSS v3.1 Base Score: 10.0 (Critical)
  • Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H

Mitigation and recommended actions

  • Immediate: No fixed release of HFS2 currently addresses this flaw. Discontinue use of HFS2 and migrate to the actively maintained HFS 3.x branch, which uses a different codebase.
  • If migration is not immediately possible:
    • Restrict network access to HFS2 instances to trusted internal hosts only (e.g., via firewall rules or VPN); do not expose HFS2 directly to the internet.
    • Run the HFS2 service account with the minimum filesystem privileges necessary, limiting the blast radius of arbitrary file access.
    • Monitor logs for requests containing macro syntax (e.g., {.load.}, {.save.}, {.append.}, {.delete.}) combined with absolute file paths, and block such requests at a reverse proxy or WAF where feasible.

References

Are you exposed?

Get a free report of your organization’s exposure to this CVE and threat

How IONIX’s External Exposure Management Platform Detects and Validates
Zero-Days to Shrink MTTR

1

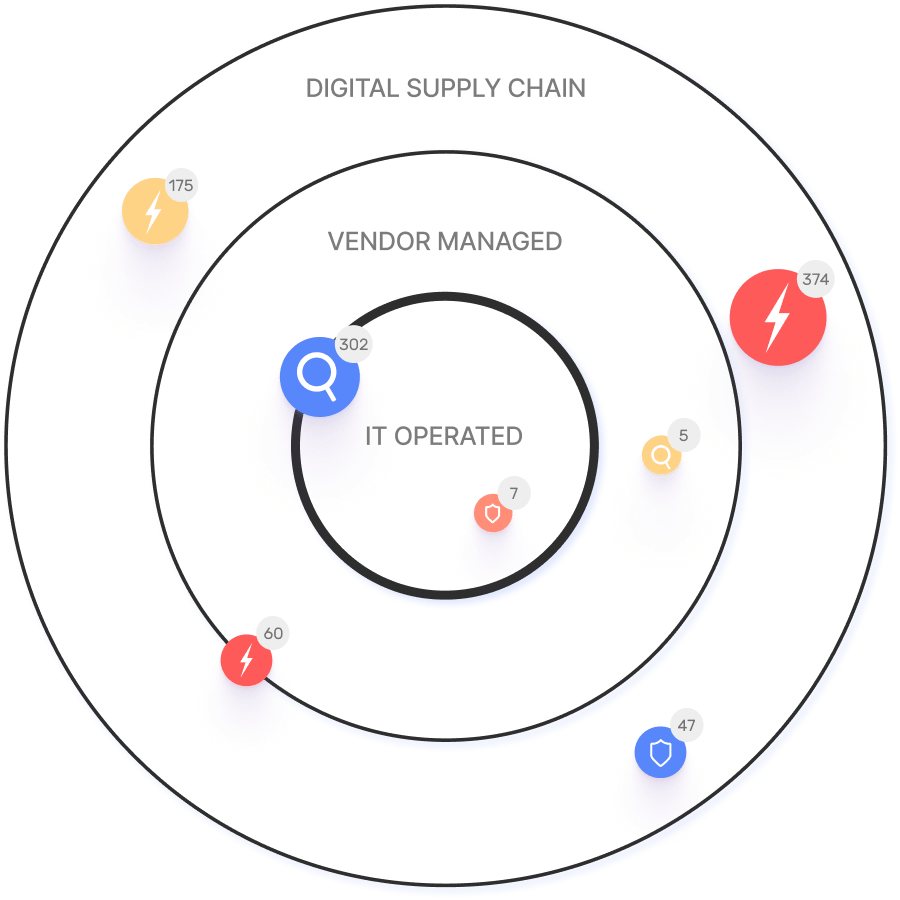
Map your entire attack surface (continously)

IONIX uses multi-factor discovery methods, including DNS analysis, certificate mapping, metadata inspection, and more, to automatically map every internet-facing asset across your environment. This includes cloud instances, third-party platforms, shadow IT, and even forgotten infrastructure that traditional tools miss.

2

Monitor for new CVEs

Dozens of threat intel feeds using agentic technology are continuously analyzed to detect the appearance of proof-of-concept code, exploit kits, and indicators of active targeting. IONIX goes further by applying AI to proactively evaluate whether emerging vulnerabilities are likely to be exploited, even before PoCs go public.

3

Identify Potential External Exposures

Not all CVEs matter. IONIX filters vulnerabilities by asking attacker-centric questions: Can it be reached from the internet? Does it require authentication? Is it being exploited in the wild? This dramatically reduces noise and focuses teams on threats that can actually be weaponized.

4

Create Safe, Scalable Exploit Validations

IONIX transforms real-world PoCs into safe, non-intrusive test payloads that can be run in production environments without disruption. These simulations are precisely targeted to the systems that are vulnerable, ensuring rapid validation without unnecessary load.

5

Execute Exploit Validations

By combining context about software stack, versioning, exposure status, and reachability, IONIX ensures that only the right payloads are executed against the right assets, maximizing efficiency and minimizing risk.

6

Drive Fast and Actionable Remediation

Results are routed through integrations with ticketing, SOAR, and SIEM tools. Issues are written in plain language, bundled into remediation clusters, and prioritized based on asset criticality, exploitability, and blast radius. This shortens mean time to remediation (MTTR) and empowers teams to act with confidence.

Are you exposed?

Get a free report of your organization’s exposure to this CVE and threat

Subscribe to Threat Center RSS

Copy/paste the link below into your preferred RSS reader or follow these instructions to subscribe to Slack alerts.

Get Real-Time CVE Alerts to Your Email

Be the first to know when new zero-days emerge